The growing threat of AI-driven cybercrime and prevention strategies

In recent years, the integration of artificial intelligence (AI) into cybercrime has significantly increased both the frequency and effectiveness of attacks. Cybercriminals are leveraging AI tools, including large language models (LLMs), to automate and enhance their malicious activities. Here we explore how AI is being used in cybercrime, with a focus on automated phishing, password spraying, and vishing, while also providing strategies to mitigate these threats.

Automated Phishing

Phishing is a cyberattack method where attackers send fraudulent messages to trick individuals into revealing sensitive information. AI has made phishing attacks more sophisticated and personalized by analysing vast amounts of data to craft highly convincing phishing emails that mimic trusted sources. These emails often feature flawless grammar and dynamic content, making them harder to detect by traditional spam filters. By automating the process, cybercriminals can execute large-scale phishing campaigns with minimal effort.

Prevention Strategies:

  • Deploy advanced email security solutions that use AI to detect and block phishing attempts.
  • Conduct regular training sessions to educate employees on recognizing phishing emails.
  • Implement multi-factor authentication (MFA) to add an additional layer of security.

Password Spraying

Password spraying is a brute-force attack method in which attackers attempt to gain access to multiple accounts by using a single common password across different login attempts. Unlike traditional brute-force attacks that repeatedly try different passwords on a single account, password spraying spreads out these attempts to avoid detection and account lockouts. This technique is particularly effective against organizations with weak password policies.

Prevention Strategies:

  • Enforce strong password policies requiring complex and unique passwords.
  • Monitor login attempts and set up alerts for unusual login patterns.
  • Implement account lockout mechanisms after a certain number of failed login attempts.

Vishing

Vishing, or voice phishing, involves attackers using phone calls to deceive individuals into disclosing personal information. With AI, cybercriminals can enhance vishing attacks by generating realistic voice messages and automating call processes. Voice-altering software and spoofed phone numbers add legitimacy to these scams, increasing their effectiveness.

Prevention Strategies:

  • Educate employees and individuals on the risks of vishing and how to recognize suspicious calls.
  • Use caller ID verification tools to detect and block spoofed numbers.
  • Encourage secure communication channels for sharing sensitive information.

Mitigating AI-Driven Cybercrime

To counter the increasing threat of AI-powered cyberattacks, organizations and individuals must adopt proactive security measures:

  • AI-Based Security Solutions: Utilise AI-powered cybersecurity tools capable of detecting and responding to threats in real time by analysing patterns and identifying anomalies.
  • Continuous Training: Regularly update and train employees on emerging cyber threats and best security practices. Awareness is a key defence against social engineering attacks.
  • Robust Authentication: Implement strong authentication measures such as MFA and biometric verification to prevent unauthorized access.
  • Regular Audits: Conduct security audits and vulnerability assessments to identify and address weaknesses in your systems.

By understanding how cybercriminals exploit AI and taking proactive steps to prevent such attacks, individuals and organizations can better protect themselves in an evolving cybersecurity landscape.
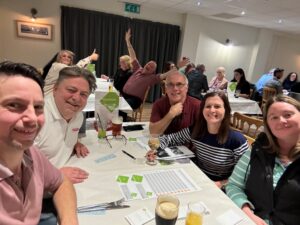
Quiz and Curry Night – A great evening for our Allied Lightbulbs Team!

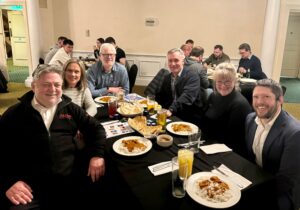
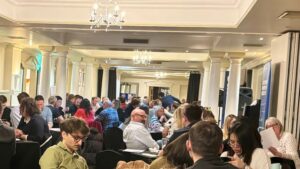
Our Allied Lightbulbs team had a fantastic time at the Quiz and Curry Night, once again expertly organized by Dutton Gregory. The event raised funds for Romsey Opportunity Group, a local charity we proudly support.

Romsey Opportunity Group provides vital support for children under five with physical, emotional, and sensory disabilities, along with their families.

Held at the Mercure Hotel in Winchester, the venue was buzzing with excitement as 26 teams competed fiercely for the coveted trophy. We were delighted to be joined by our friends from Hampshire Business Computers, who brought along a few extra ‘brains’ to strengthen our team!

A huge congratulations to the winners, and well done to everyone who took part. Thanks to the generosity of attendees, the event raised an impressive £2,220, helping Romsey Opportunity Group continue its invaluable work.
Thank you for a fantastic evening—see you at the next one!


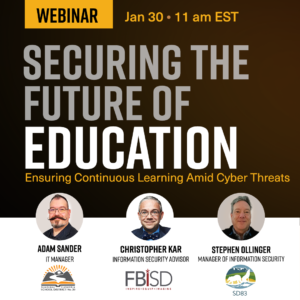
Cybersecurity Webinar: Protecting schools against emerging threats

Ransomware attacks and data breaches are hitting schools harder than ever, jeopardizing student safety, privacy, and academic progress. Ignoring these threats puts your entire learning environment at risk.

On Thursday 30th January at 4pm GMT, join three leading cybersecurity experts for a webinar:

Securing the Future of Education: Ensuring Continuous Learning Amid Cyber Threats

They will reveal actionable strategies to:

  • Prevent relentless ransomware from halting classes and exams
  • Safeguard sensitive student records from theft and exposure
  • Maintain trust and keep critical learning systems fully operational

The threats are real—and evolving. Don’t let your institution become the next headline.

Registration Link: https://eu1.hubs.ly/H0fwcJ50

In partnership with BullWall


Top 5 advantages of IP phones

IP phones, also called VoIP phones (Voice over Internet Protocol), are communication devices that enable voice calls and other services to be transmitted over the internet instead of traditional analog phone lines.

Here are top 5 advantages of IP phones

  1. Cost Savings

IP phones greatly reduce call costs, particularly for long-distance and international calls. They also eliminate the need for costly hardware and the maintenance associated with traditional phone systems..

  1. Scalability

As your business grows, you can easily add or remove users without requiring extra infrastructure. You pay only for the services you need, offering flexibility and cost-effectiveness.

  1. Mobility and Remote Work

Employees can make and receive calls from anywhere with an internet connection, making it ideal for remote work or businesses with multiple locations. Mobile integration lets calls be managed from personal devices while keeping professional numbers intact.

  1. Advanced Features

IP phones provide features such as voicemail-to-email, call forwarding, conference calling, and integration with business tools (like CRM software), all of which enhance productivity and communication.

  1. Unified Communications

IP phones integrate smoothly with other communication tools (such as video conferencing and messaging), creating a unified platform for all business communications and enhancing collaboration and efficiency.


Learn more here


How to prevent password spraying attacks

What is a password spraying attack?

Password spraying is a distinct type of brute force attack that targets multiple accounts using a single password attempt, rather than repeatedly attempting numerous passwords on a single account. This method is often effective because many users rely on simple, predictable passwords such as “password” or “123456.”

In many organizations, account lockout policies are triggered after a certain number of failed login attempts. However, password spraying circumvents these lockouts by testing one password across numerous accounts, avoiding detection and lockout mechanisms designed for traditional brute force attacks.

Unlike attacks that focus on a single user, password spraying can target millions of accounts simultaneously. The process is typically automated and often executed over an extended period to further evade detection.

These attacks are particularly common in scenarios where applications or administrators assign default passwords to new users. Platforms such as single sign-on (SSO) systems and cloud-based services are also frequent targets due to their centralized access and widespread adoption.

While seemingly straightforward, password spraying remains a favoured technique among even the most advanced cybercriminal groups due to its efficiency and high success rate.

How does a password spraying attack work?

Password spraying attacks typically involve these steps:

Step 1: Cybercriminals purchase a list of usernames or create their own list

To carry out a password spraying attack, cybercriminals often begin by purchasing lists of usernames stolen from various organizations. It is estimated that over 15 billion credentials are currently available for sale on the dark web.

Alternatively, attackers may generate their own lists by identifying common corporate email address formats, such as firstname.lastname@companyname.com, and cross-referencing these with employee information found on platforms like LinkedIn or other publicly available sources.

Cybercriminals frequently target specific employee groups, such as those in finance, administration, or executive leadership (C-suite), as these targeted approaches tend to yield higher success rates. Companies or departments that use single sign-on (SSO) or federated authentication protocols—such as logging into one platform with credentials from another—or those lacking multi-factor authentication (MFA) are particularly vulnerable to such attacks.

Step 2: Cybercriminals obtain a list of common passwords

Password spraying attacks incorporate lists of common or default passwords. It’s relatively straightforward to find out what the most common passwords are – various reports or studies publish them each year, and Wikipedia even has a page which lists the most common 10,000 passwords. Cybercriminals may also do their own research to guess passwords – for example, by using the name of sports teams or prominent landmarks local to a targeted organisation.

Step 3: Cybercriminals try out different username/password combinations

Once cybercriminals have compiled a list of usernames and passwords, their goal is to test these combinations until they find one that works. The process is typically automated using password spraying tools. To bypass lockout policies and IP address blockers that limit repeated login attempts, attackers test one password across multiple usernames before moving on to the next password in their list.

Signs of a password spraying attack

Password spraying attacks often result in a high volume of failed authentication attempts across multiple accounts. Organizations can identify such activity by analysing authentication logs for repeated login failures involving valid accounts on systems and applications.

Overall, the main signs of a password spraying attack are:

  • A high volume of login activity within a short period.
  • A spike in failed login attempts by active users.
  • Logins from non-existent or inactive accounts.


How to defend against password spraying attacks

Organisations can protect themselves from password spraying attacks by following these precautions:

Implement a strong password policy

By enforcing the use of strong passwords, IT teams can minimise the risk of password spraying attacks.

Ensuring strong lockout policies

Setting a suitable threshold for the lockout policy at domain level defends against password spraying. The threshold needs to strike a balance between being low enough to prevent attackers from making multiple authentication attempts within the lockout period, but not so low that legitimate users are locked out of their accounts for simple errors. There should also be a clear process for unlocking and resetting verified account users.

Adopt a zero trust approach

The cornerstone of the zero trust approach is providing access to only what is required at any given time to complete the task at hand. Implementing zero trust within an organisation is a key contribution towards network security.

Use a non-standard username convention

Avoiding selecting obvious usernames like john.doe or jdoe – which are the most common methods for usernames – for anything other than email. Separate non-standard logins for single sign on accounts is one way to evade attackers.

Use biometrics

To prevent attackers from exploiting the potential weaknesses of alphanumeric passwords, some organisations require a biometric login. Without the person present, the attacker can’t log in.

Look out for patterns

Make sure any security measures in place can quickly identify suspicious login patterns, such as a large volume of accounts attempting to log in simultaneously.

Using a password manager can help

Passwords are intended to protect sensitive information from criminals. However, the average user today has so many passwords that it can be difficult to keep track of them all – particularly as each set of credentials is supposed to be unique.

To try to keep track, some users make the mistake of using obvious or easy-to-guess passwords, and often use the same password across multiple accounts. These are precisely the type of passwords that are vulnerable to password spraying attacks.

Attacker capabilities and tools have evolved considerably in recent years. Computers are much faster today at guessing passwords. Attackers use automation to attack password databases or online accounts. They have mastered specific techniques and strategies that yield more success.

For individual users, using a password manager, such as N-Able PassPortal, can help. Password managers combine complexity and length to offer up hard-to-crack passwords. They also eliminate the burden of having to remember different login details and moreover, a password manager will help to check whether there is a repetition of passwords for different services. They are a practical solution for individuals to generate, manage, and store their unique credentials.


A manufacturing company digitises their delivery notes process

Allied Office Machines help WRES, a precision fabrication company, to streamline their delivery notes and work orders processes by implementing GlobalCapture software.

GlobalCapture is a document capture and workflow automation system designed to digitise business processes within an organization.

WRES’ business system is configured to create a bar code when the work orders and the delivery notes are generated. After the documentation has been signed, GlobalCapture will read and recognise the barcode and automatically attach the document to the right customer record. The main benefits are reduced processing time, improved staff productivity and ISO compliance

Lewis Hamer, Director at WRES, commented: ” Before implementing scanning software, our finance team spent hours each day manually scanning signed work orders and delivery notes. With GlobalCapture, this entire process now takes just minutes. The team is thrilled to have eliminated the tedious, time-consuming manual work. We are now exploring other areas of the business that could benefit from this streamlined solution.”

Steve Drayson, MD at Allied Office Machines, added: ” At Allied, our focus is always on adding value for our customers by providing solutions that truly meet their needs and improve their operational efficiency. We are very pleased with the outcome and the positive impact it has had on their daily working practices”

Picture: Lewis Hamer from WRES and Frankie Girardelli from Allied Office Machines


The Lightbulbs team in action again in a charity quiz

The Allied Office Machines’ Lightbulbs team recently participated in another charity quiz in support of Rowans Hospice.charity quiz Expertly organized by Glanvilles Legal Services, the event brought together numerous local businesses to raise funds for this worthy cause. Fun was had by all, despite the slightly ‘dimmed’ performance of our team on the scoreboard 😂. We are loving the enthusiasm of our friends at Lawson Financial Ltd on the table behind 👋

Rowans Hospice provide palliative and end of life care to the highest quality for those living with a life-limiting illness in the Southeast of Hampshire. Their highly trained hospice carers help to improve quality of life for the patient by easing physical symptoms as well as offering psychological, spiritual and social support to both patients and their loved ones.

#charity #community #giving back


Which Microsoft products are reaching end of support in 2025?

As we approach 2025, several Microsoft products are scheduled to reach their end of life (EOL). This means that after their EOL date, these products will no longer receive security updates, non-security updates, or technical support from Microsoft.

Products reaching their end of life in 2025


Windows 10:

Windows 10 Home and Pro

Windows 10 Enterprise and Education

Windows 10 IoT Enterprise

EOL Date: October 14, 2025


Microsoft Office:

Office 2016 and Office 2019 suites

Standalone applications (e.g., Word, Excel, PowerPoint)

EOL Date: October 14, 2025


Microsoft Exchange Server:

Exchange Server 2016 and 2019

EOL Date: October 14, 2025


Microsoft Dynamics:

Dynamics CRM 2015

Dynamics NAV 2015

Dynamics SL 2015

EOL Date: Various dates in 2025


Visual Studio:

Visual Studio 2015

Visual Studio 2022 (LTSC channel)

EOL Date: Various dates in 2025


SQL Server:

SQL Server 2012 (Extended Security Update Year 3)

SQL Server 2014 (Extended Security Updates Year 1)

EOL Date: Various dates in 2025


Preparing for the transition

To ensure a smooth transition and avoid potential security risks, it’s important to start planning your upgrades now. Here are some steps you can take:

  1. Assess your current systems: Identify which of your systems and applications are running on the products listed above.
  2. Plan your upgrades: Determine the best upgrade path for your organization. This might involve moving to newer versions of the software or transitioning to cloud-based solutions like Microsoft 365.
  3. Consult with experts: Reach out to IT professionals who can provide guidance and support throughout the upgrade process.

Why us?

We can be an invaluable partner during this transition. Here’s why:

  • Expertise: We have extensive experience in managing IT upgrades and migrations, ensuring minimal disruption to your business operations.
  • Customized Solutions: We can provide tailored solutions that meet the specific needs of your organization, whether you’re a small business or a large enterprise.
  • Ongoing Support: We offer ongoing support and maintenance services to keep your systems running smoothly long after the upgrade is complete.

By partnering with us, you can ensure that your transition to newer Microsoft products is seamless and efficient. Don’t wait until the last minute—start planning your upgrades today to stay ahead of the curve.

If you have any questions or need further assistance, feel free to contact Steve at s.drayson@aomltd.co.uk or 01794 526088


Looking to simplify your purchasing and reduce the hassle of managing multiple suppliers?

We are now able to offer a single point of contact for all your technology needs including copiers and printers, document automation software, cybersecurity, IT support, IP phones and leased lines.Reduce number of suppliers

What are the benefits of reducing the number of suppliers?

Cost Savings

Reduced Administrative Costs: Managing fewer suppliers reduces administrative overhead associated with procurement processes, invoicing, contract management and communication.

Enhanced Quality and Consistency

Consistent Quality Standards: Reducing the number of suppliers can help ensure more consistent product or service quality. This is because fewer suppliers can be managed more closely to meet specific quality standards.

Simplified Logistics: Managing fewer suppliers simplifies logistics, making supply chain management more efficient, agile and less prone to errors or delays.

Reduced Risks

Minimised Supplier Risk: With fewer suppliers to manage, companies can more effectively assess and mitigate risks such as financial instability, compliance issues or ethical concerns.

Compliance and Sustainability

Easier Compliance Management: With fewer suppliers, it is easier to manage and enforce compliance with regulations, industry standards and company policies.

Sound good? Contact Steve Drayson on 01794 526088 or email s.drayson@aomltd.co.uk.


Allied Office Machines and Hampshire Business Computers announce a strategic partnership

Allied Office Machines are delighted to announce a strategic partnership with Hampshire Business Computers, a leading IT provider in the Hampshire region.

Steve Drayson from Allied and Olly Ross from HBC and the team

This collaboration between Allied Office Machines and Hampshire Business Computers aims to combine their strengths and expertise. With Allied Office Machines’ extensive experience in office equipment and business process automation and Hampshire Business Computers’ proven capabilities in IT infrastructure, cybersecurity and cloud based phone systems, the alliance is set to provide exceptional value to clients.

“We are excited to join forces with Hampshire Business Computers,” said Steve Drayson, MD at Allied Office Machines. “This partnership allows us to expand our service offerings and provide a more comprehensive IT solution to our clients. Both companies share a commitment to excellent customer satisfaction and support for local community and  charities.”

Olly Ross, Sales Director of Hampshire Business Computers, added: “Partnering with Allied Office Machines is a fantastic opportunity to bring together our complementary skills and expertise. Our combined resources will enable us to offer a broader range of services and drive innovation in the technology solutions we provide.”

Picture: Steve Drayson from Allied Office Machines and Olly Ross from Hampshire Business Computers and the team